Over the past decade, digital communication has been shaped by a simple assumption: providers must see everything. Identity, metadata, behavioural signals, device fingerprints, timestamps visibility has been treated as a prerequisite for trust.
But what if visibility is the problem?
In high-risk environments, social platforms, organisational communication, and investigative contexts, visibility creates structural vulnerabilities: impersonation, inference, metadata leakage, and provider-side surveillance. As the attached paper states, “visibility-based systems assume that communication must occur within observable channels”, a design choice that makes impersonation and inference “structurally impossible” .
The Identity Constructed Communication Architecture (ICCA) proposes a different path—one that does not extend Zero Trust, but replaces its foundational assumptions entirely.
The Core Shift: Identity Becomes the Channel
Traditional systems create channels first and attach identity to them. ICCA reverses this logic.
ICCA constructs communication channels directly from identity rather than from provider-visible infrastructure.
This identity-first geometry means:
- Channels cannot be spoofed
- Channels cannot be replicated
- Channels dissolve immediately after use
- No metadata persists
This is not “more secure messaging.” It is a new communication geometry.
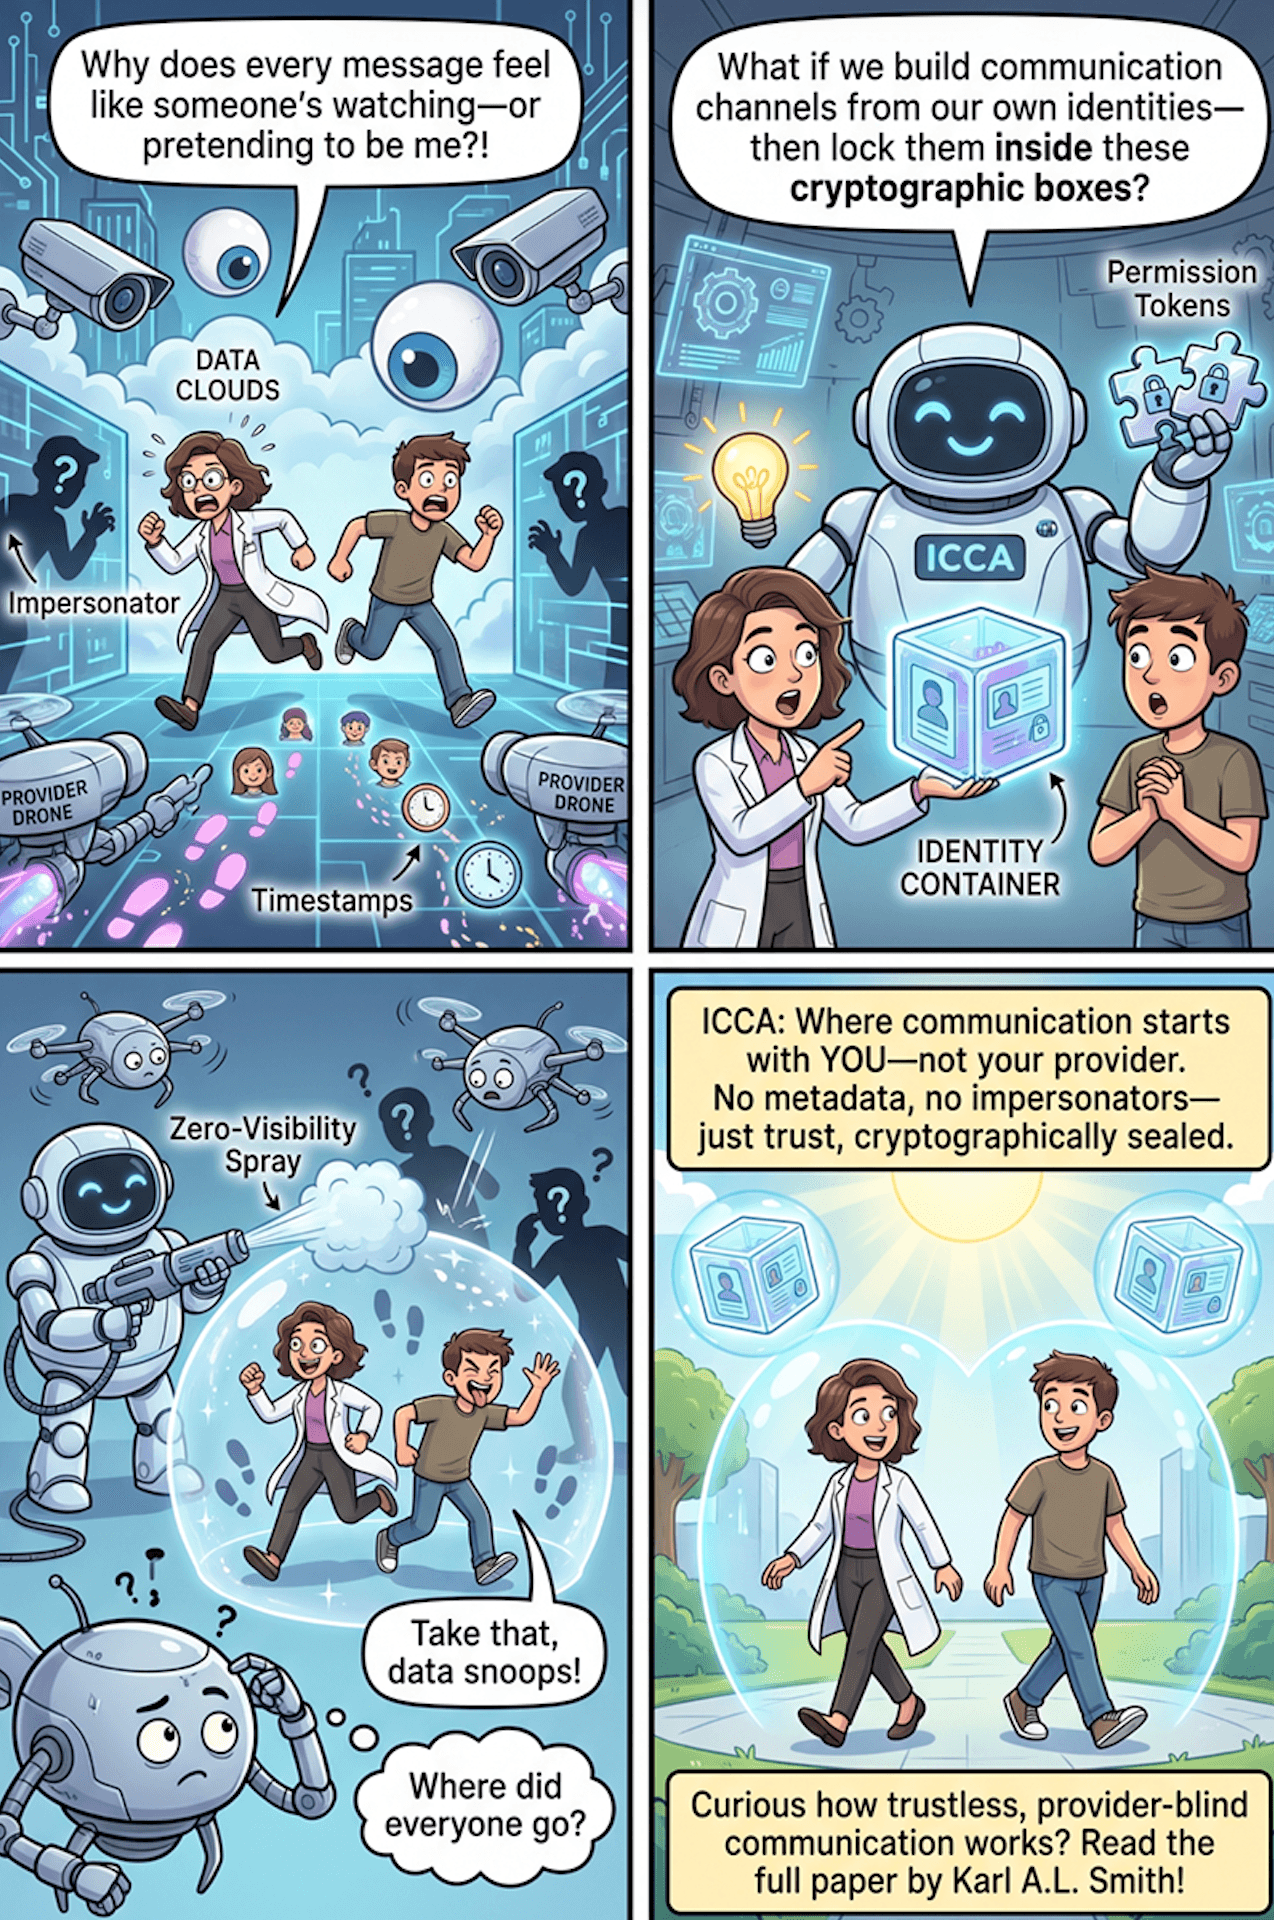
Zero-Knowledge Identity Containers: Identity Without Exposure
ICCA introduces sealed cryptographic identity containers that store identity, organisational membership, and context without exposing anything to the provider.
These containers remain opaque to the provider… no metadata is exposed, no organisational structure is visible.
This eliminates:
- identity visibility
- behavioural inference
- social-graph reconstruction
- metadata-based profiling
In ICCA, identity is proven, never revealed.
Blind Provider Operation: Infrastructure Without Visibility
One of ICCA’s most radical departures is the blind provider model.
The provider cannot see:
- who is communicating
- when communication occurs
- how often
- any relationships
- any behavioural signals
As the paper states:
Provider-side inference becomes structurally impossible because visibility is eliminated rather than restricted.
This is not privacy by policy. It is privacy by architecture.
Zero Metadata Transport: The End of Inference
ICCA eliminates all metadata surfaces:
- IP addresses
- device fingerprints
- timestamps
- routing information
- session identifiers
This makes inference attacks, behavioural analytics, and impersonation structurally impossible, not merely mitigated.
ICCA’s zero metadata transport layer eliminates IP addresses, device fingerprints, timestamps, routing information and social-graph indicators.
This is the first architecture to treat metadata as a security liability rather than an operational necessity.
Why ICCA Is Not Zero Trust 2.0
Zero Trust assumes visibility. ICCA removes it.
Zero Trust requires continuous verification. ICCA requires cryptographic sufficiency.
Zero Trust mitigates impersonation. ICCA makes impersonation impossible.
The paper is explicit:
ICCA is not derived from visibility-based security research and does not extend Zero Trust.
ICCA is a post-visibility architecture.
All Me: The First ICCA Implementation
All Me operationalises ICCA as a trustless, identity-anchored communication platform. It demonstrates that:
- communication can be metadata-free
- providers can operate blind
- identity can be sealed
- impersonation can be structurally eliminated
All Me is the first example of an Independent Identity Network (IIN)—a new category of communication systems where identity is the origin of interaction and visibility is structurally impossible.
Why This Matters for the Future of Digital Trust
ICCA’s implications extend far beyond social platforms:
- critical infrastructure communication
- zero-knowledge enterprise messaging
- high-risk investigative work
- multi-cloud coordination without provider exposure
- hardware-level trustless communication terminals
The paper notes:
ICCA establishes a new trust geometry with implications for digital rights, privacy governance and the legal status of identity in communication systems.
This is not an incremental improvement. It is a structural alternative to visibility-based communication.
A Post-Visibility Future
ICCA shows that trust does not require visibility. It requires cryptographic proof.
It shows that communication does not require metadata. It requires identity-anchored channels.
And it shows that providers do not need to see anything to operate securely.
The future of digital trust will not be built on more monitoring, more analytics, or more visibility. It will be built on architectures where visibility is impossible by design.
Related papers
- Identity Constructed Communication Architecture (ICCA) – A Trustless, Model for Provider Blind Communication on SSRN
- Identity Constructed Communication Architecture (ICCA) – A Trustless, Model for Provider Blind Communication on Academia
- Situational Awareness Commerce: A Post-GUI Model for Object-Driven, Identity-Free Transactions on SSRN
- Situational Awareness Commerce: A Post-GUI Model for Object-Driven, Identity-Free Transactions on Academia