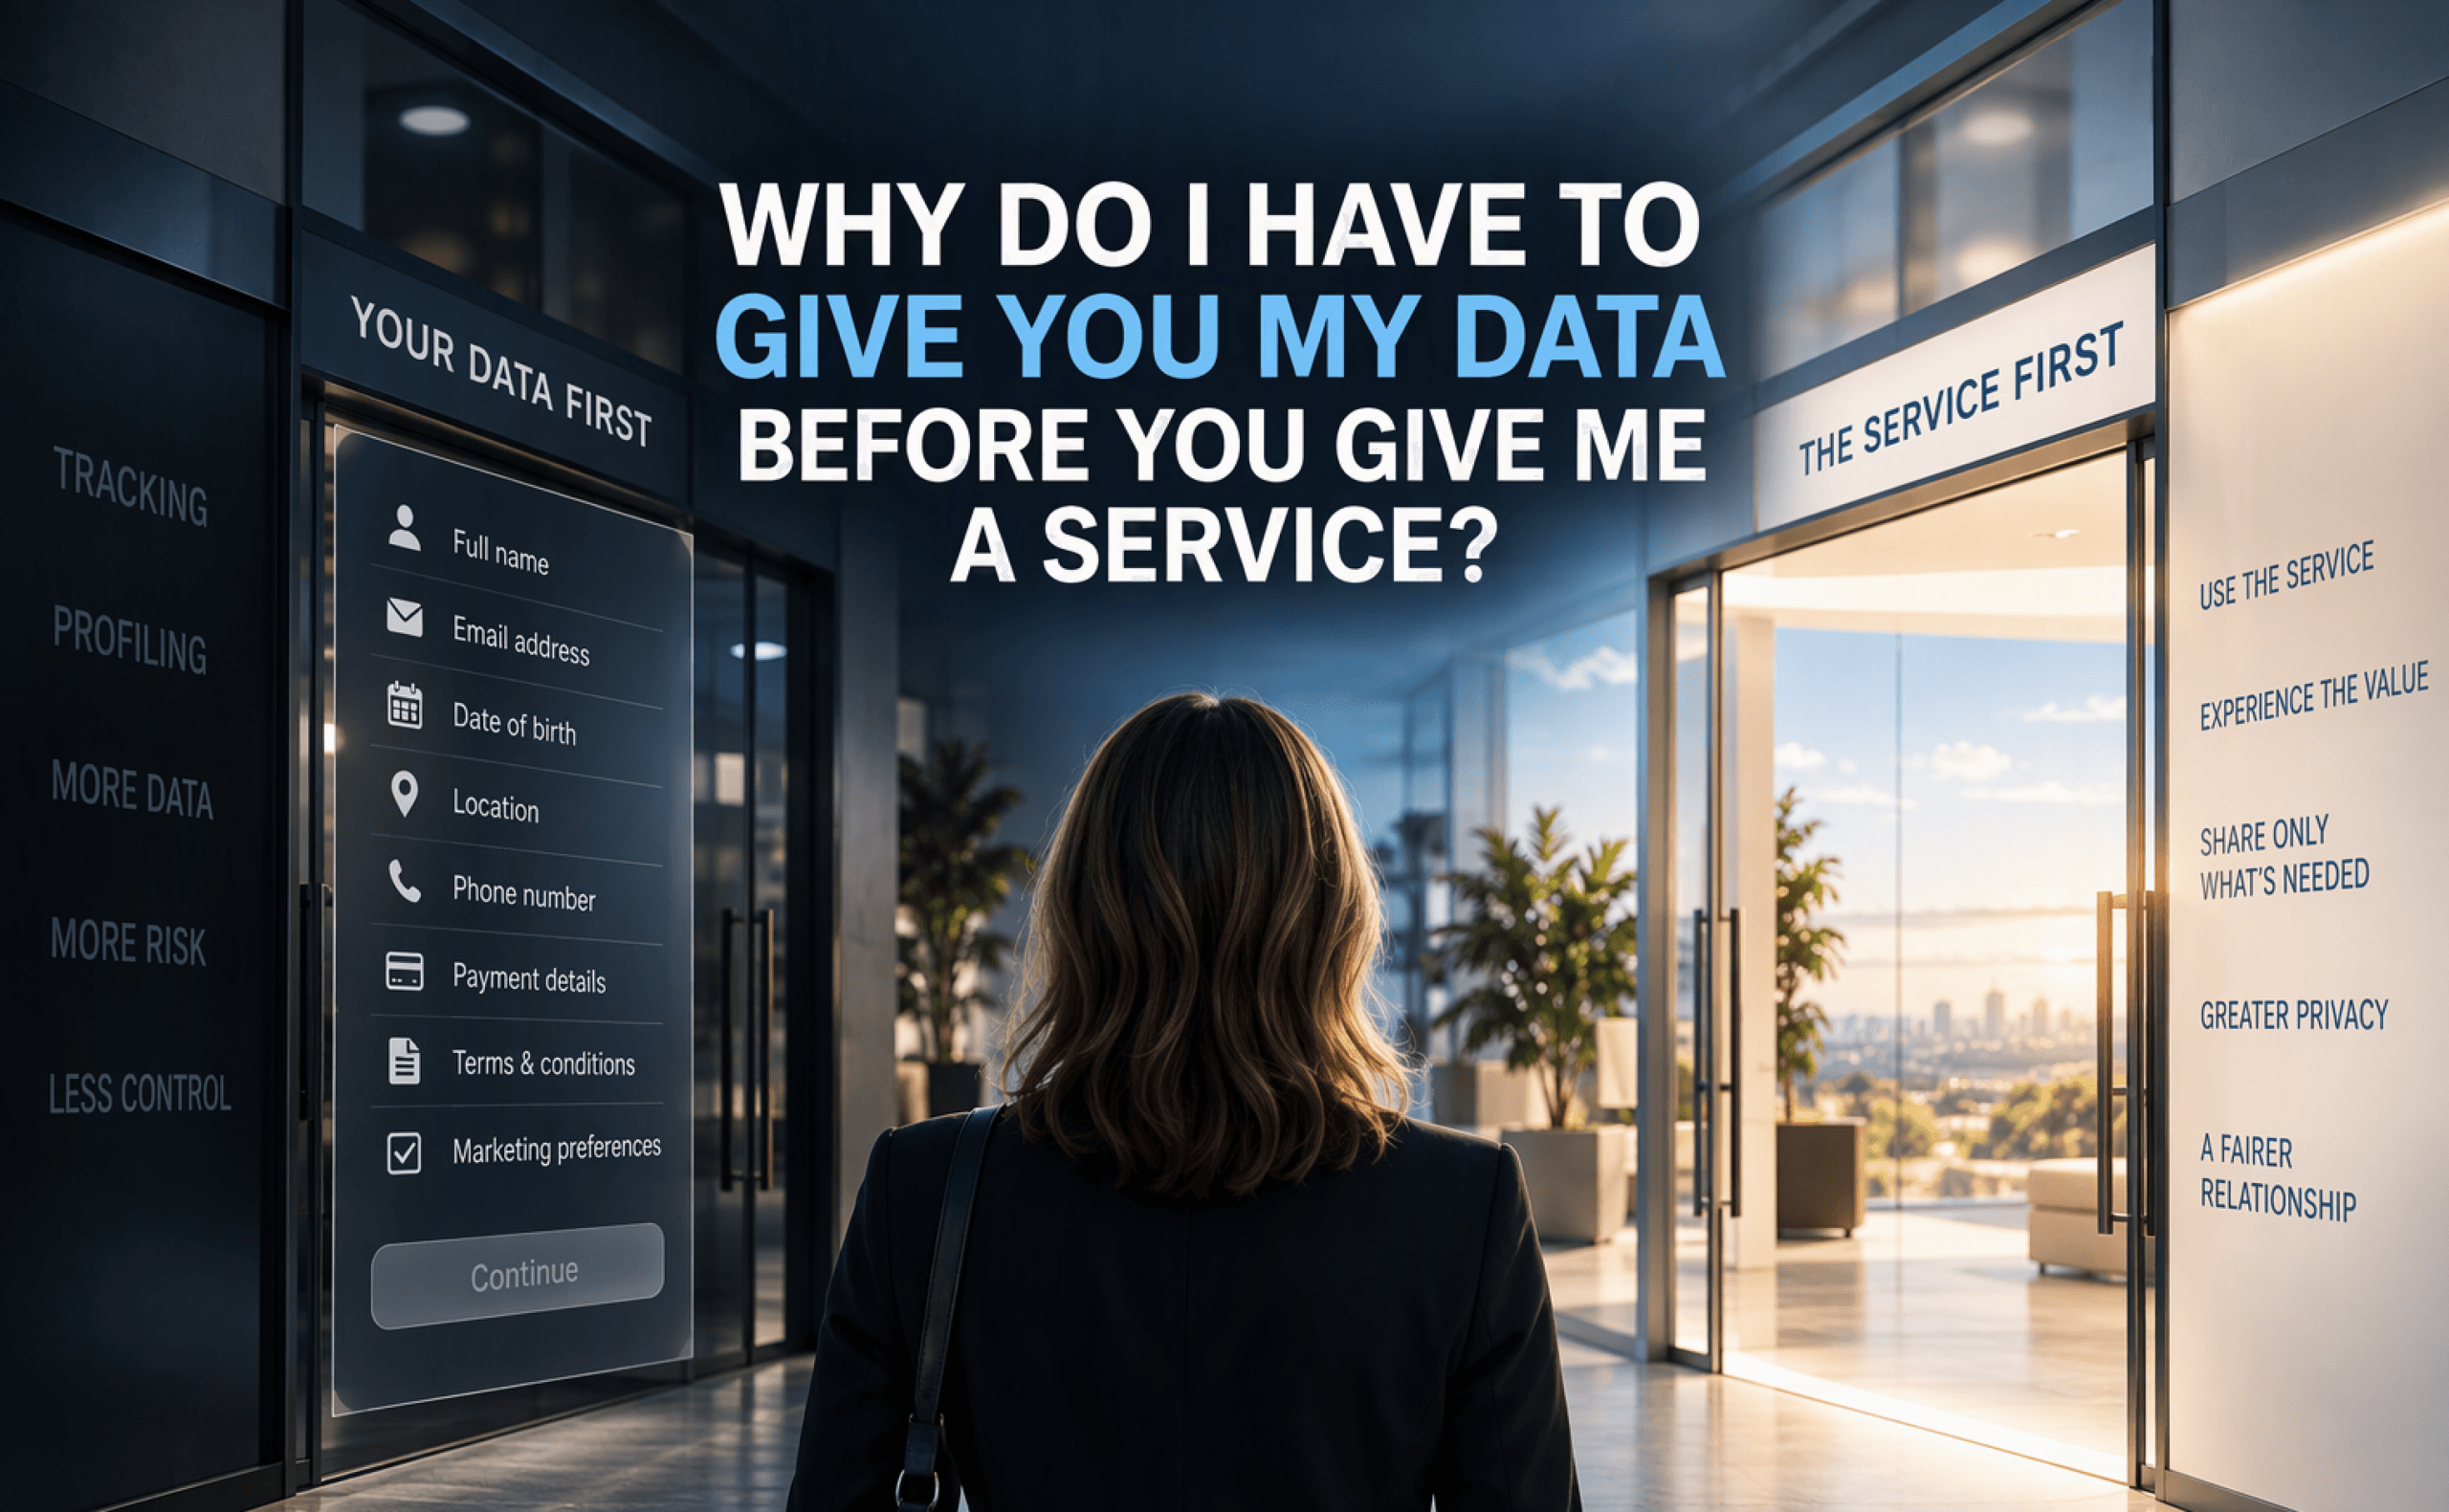
Think about the last time you tried a new digital service.
Before you had experienced its value, you were probably asked for something.
- Your name.
- Your email address.
- Your date of birth.
Perhaps your location, telephone number or payment details.
Then came the terms and conditions, privacy notice, cookie choices and permissions.
All before the relationship had really begun.
We have become so accustomed to this exchange that it feels normal:
My data first. Your service second.
But why?
What if we reversed the assumption?
Imagine walking into a shop and being required to complete a personal information form before you were allowed to browse.
Most of us would question it.
Yet digitally, we routinely provide information simply to enter.
This creates an interesting question for organisations:
How much information do we genuinely need from a customer to provide the thing they actually came for?
For a new business or greenfield platform, that question can be asked before the operating model becomes dependent on collecting information.
Instead of starting with:
What data can we collect?
Start with:
What is the minimum we need to make this interaction work?
That changes the relationship from the beginning.
For existing organisations, the question is harder
Established businesses have years of processes, technology, analytics, customer records and governance built around data.
Removing unnecessary collection may therefore appear difficult.
But there is another side to the equation.
Every piece of information an organisation chooses to retain becomes something it may need to protect, govern, secure and eventually dispose of.
So the executive question is not simply whether data has value.
It is whether every piece of data creates enough value to justify the responsibility that comes with holding it.
From collecting people to serving people
This is where Identity First, Data Last becomes an interesting design principle.
It challenges the assumption that knowing more about someone automatically produces a better digital relationship.
Sometimes the organisation needs to know something.
Sometimes it merely needs to know that a requirement has been satisfied.
And sometimes it may not need to know anything at all.
Those are very different relationships.
The opportunity is therefore not simply better privacy.
It is to rethink the exchange between an organisation and the people using its services.
Provide the service. Ask for information when there is a genuine reason. Don’t make data collection the price of admission.
That may be particularly important as customers become increasingly aware of just how much information they leave behind simply by participating in digital life.
A question for leaders
Look at the first five minutes of your own customer journey.
How much information are you asking people to provide before you’ve provided them with any value?
And then ask the uncomfortable second question:
How much of it do you genuinely need?
That is the adoption question behind ICCA Design Principles: Identity First, Data Last.
The underlying ICCA work is being openly shared under a Creative Commons Attribution-ShareAlike 4.0 licence, encouraging discussion, challenge, adaptation and further development.
The paper describes the architectural principle. This article asks what adopting that principle could mean for people and organisations.
#ICCA #DigitalTrust #PrivacyByDesign #CustomerExperience #Leadership #DataGovernance #DigitalTransformation #DataPrivacy #Innovation #CreativeCommons